CIS Controls Assessment
Evaluate your organization's cybersecurity posture against the industry-standard CIS Critical Security Controls framework.
Why This Matters
The Cost of Not Knowing Your Posture
A CIS assessment isn't just a compliance exercise — it's a risk management decision with measurable financial and legal consequences.
of top attack types — malware, ransomware, web app attacks, insider misuse, and targeted intrusions — are blocked by implementing CIS IG1 safeguards alone. Full implementation reaches 91%.
Source: CIS Community Defense Model v2.01
Ohio, Utah, Connecticut, Iowa, and Texas have enacted cybersecurity Safe Harbor laws. Organizations that follow CIS Controls gain an affirmative legal defense against breach-related lawsuits.
Source: CIS.org — Texas Safe Harbor Law, Aug 20252
One CIS assessment maps directly to HIPAA, CMMC, and NIST CSF. FrameworkMapper's crosswalk reports let you satisfy multiple compliance requirements from a single assessment engagement.
FrameworkMapper framework mapping
A traditional CIS assessment is a significant investment, while ransomware recovery for a small-to-mid organization can be devastating. FrameworkMapper makes structured assessment accessible — a fraction of a percent of breach exposure.
Source: IBM Cost of a Data Breach Report 20253
What are the CIS Controls?
The CIS Critical Security Controls are a prioritized set of actions developed by the Center for Internet Security that collectively form a defense-in-depth set of best practices to mitigate the most common cyber attacks.
18 Control Areas
Organized into 18 critical security control areas covering everything from inventory management to incident response and penetration testing.
153 Safeguards
Each control contains specific safeguards — actionable security measures that can be implemented and measured within your organization.
Prioritized by Risk
Controls are prioritized based on real-world attack data, focusing your efforts on the actions that provide the greatest security benefit.
Implementation Groups (IG)
CIS Controls are organized into three Implementation Groups based on organizational size, resources, and risk profile. This helps you prioritize which safeguards to implement first.
Essential Cyber Hygiene
The foundational set of cyber defense safeguards that every organization should implement. Designed for small organizations with limited IT resources.
Extended Hygiene
Additional safeguards for organizations with moderate resources that handle sensitive data and face more sophisticated threats.
Advanced
The complete set of safeguards for organizations with significant security resources that must protect highly sensitive data.
Who Should Use This Assessment?
Organizations of Any Size
From small businesses to large enterprises looking to establish or improve their security baseline.
Compliance-Focused Teams
CIS Controls map to many regulatory frameworks including NIST, ISO 27001, PCI-DSS, and HIPAA.
Budget-Conscious Security Teams
The prioritized approach helps you focus limited resources on the most impactful security controls.
Security Program Benchmarking
Track your security maturity over time and demonstrate progress to leadership and stakeholders.
How the Assessment Works
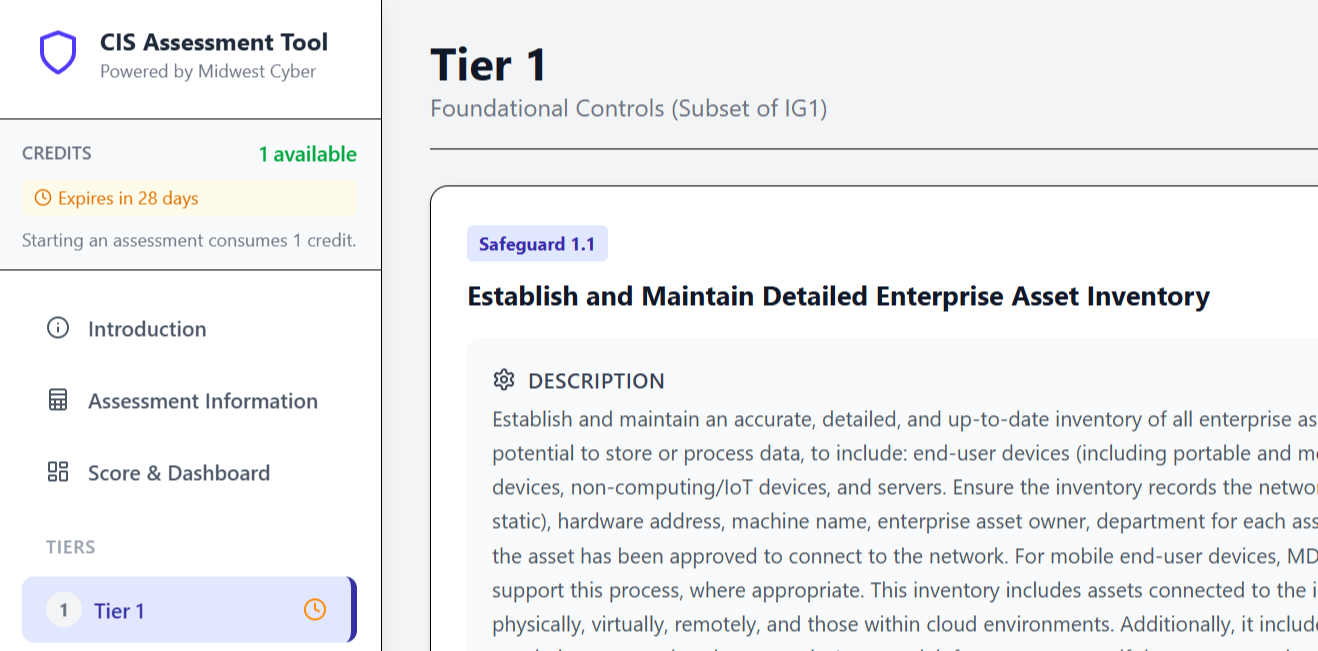
Our assessment tool guides you through all 153 safeguards with a simple, intuitive interface. Save your progress and return anytime.
Select Your Tier
Navigate through 10 progressive tiers, each building on the security foundations of the previous tier.
Rate Each Safeguard
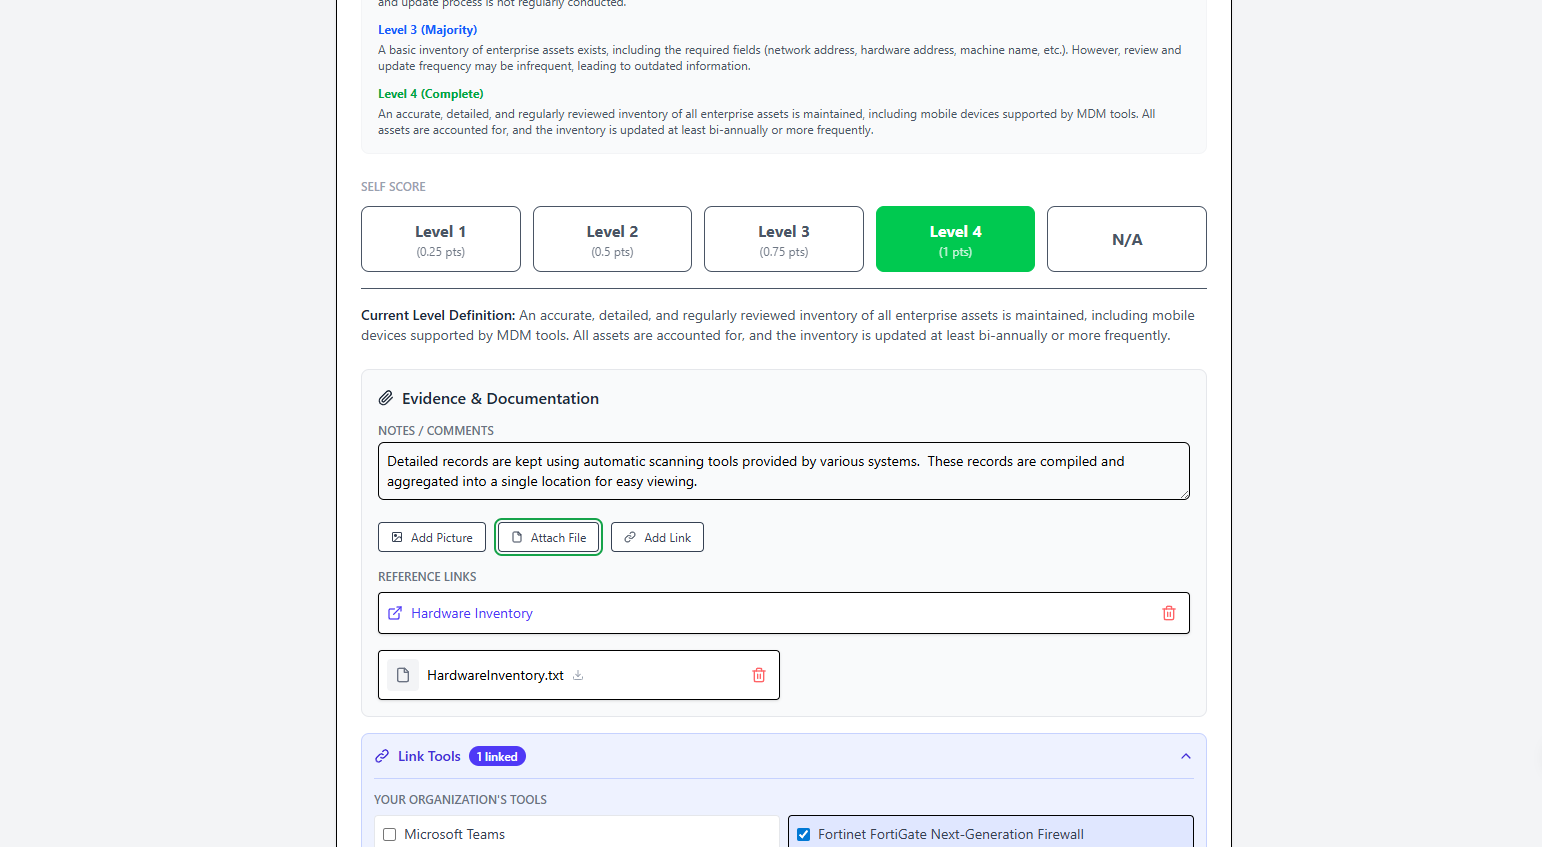
For each safeguard, indicate your implementation level: Not Implemented, Partially, Mostly, or Fully Implemented.
Add Notes & Evidence
Document your implementation details, responsible parties, and any evidence for each safeguard.
Review & Generate Reports
Once complete, generate professional PDF reports and secure backups of your assessment data.
Time Estimate
A complete assessment typically takes 2-8 hours, depending on your organization's complexity and how thoroughly you document each safeguard.
What to Have Ready
- Current IT asset inventory
- List of security tools in use
- Access to security policies
- Knowledge of current processes
What You'll Receive
Upon completing your assessment, you'll have access to comprehensive reports that help you understand your security posture and plan improvements.
Executive Summary
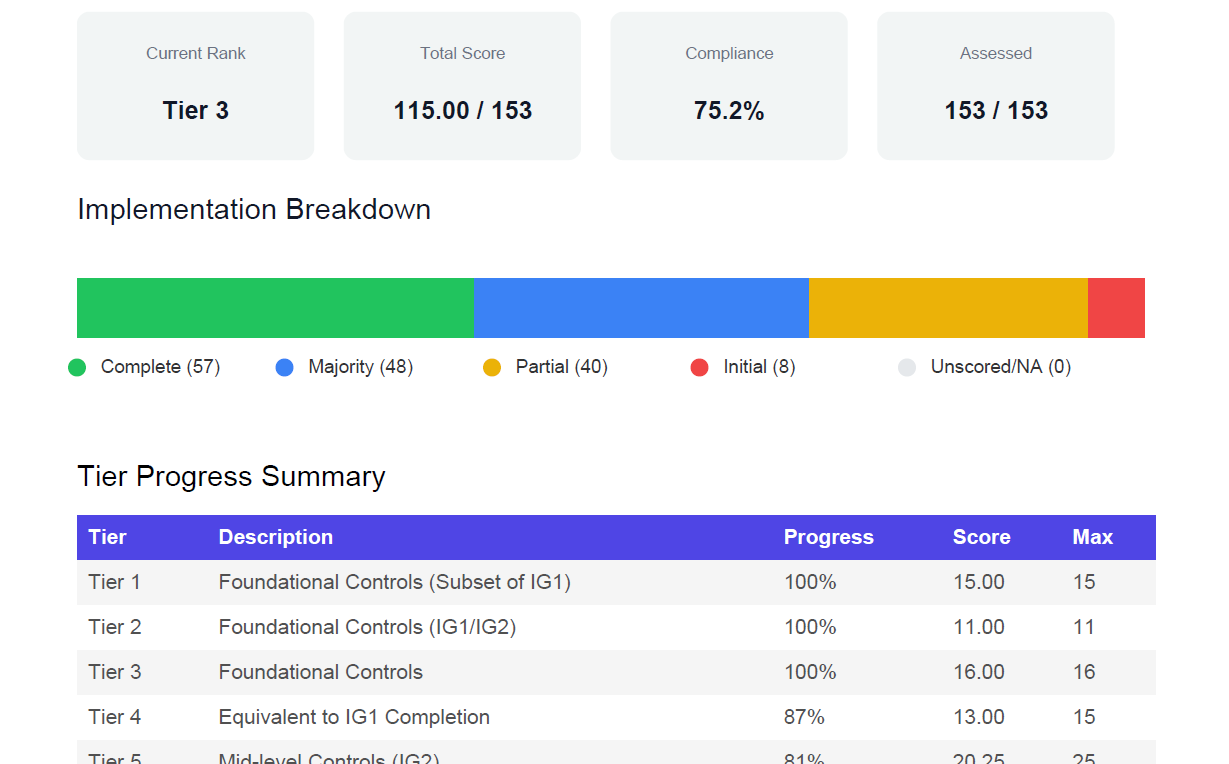
A high-level overview designed for leadership and stakeholders. Includes overall maturity scores, Implementation Group progress, and visual charts showing your security posture at a glance.
- Overall maturity score
- IG1/IG2/IG3 breakdown
- Visual progress charts
Detailed Assessment
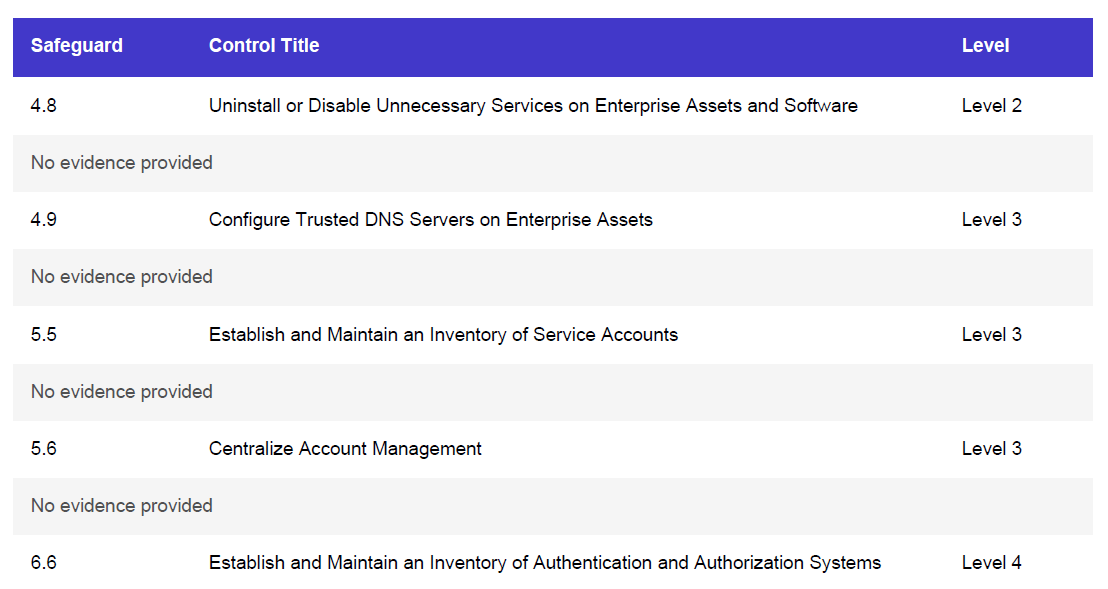
A comprehensive report listing every safeguard with your implementation rating, notes, and evidence. Perfect for technical teams and audit documentation.
- All 153 safeguards
- Your notes & evidence
- Per-control scores
Encrypted Backup
A password-protected JSON file containing all your assessment data. Use it to restore your assessment on any device or transfer between accounts.
- AES-256 encryption
- Complete data export
- Easy restore process
Every Assessment Includes
Beyond your core deliverables, every CIS Controls assessment unlocks a full suite of analytics, executive reporting, and remediation planning tools through the Analysis Dashboard.
Stakeholder-Ready Outputs
Communicate findings to executives, boards, and auditors with presentation-ready reports.
- Executive Summary Report (PDF)
- Verifiable Certificate (PDF · public verification)
- Executive Dashboard
Remediation Planning
Prioritize and track remediation with actionable gap optimization and milestone planning.
- Gap Optimization
- POAM — Plan of Action & Milestones (PDF/CSV)
- Tool Coverage & Recommendations
- Risk Score Analysis
Visual Analytics
Explore your security posture through interactive dashboards and visualizations.
- Safeguard Analysis
- Heatmap View
- Radar Chart
- Tool Usage Analysis
- Tool Effectiveness Analysis
Beyond Compliance
See Your Results Through an Attacker's Eyes
Completing your assessment unlocks FrameworkMapper's threat-informed views — the same control scores, re-read against real adversary behavior from MITRE ATT&CK® and curated threat intelligence.
Threat Lens & Adversary Likelihood
Advanced reports that map your control scores to attacker techniques and rank which adversaries are most likely to succeed against you.
Threat-Informed Executive Report
A board-ready PDF with your Attack Surface Coverage Score (ASCS) and kill-chain exposure, computed from your actual answers.
Incident Response Packet
Your assessment answers and evidence pre-fill a Responder Brief and evidence bundle, so responders can act on day one. Learn more
Included With Your Subscription
Runs on the FrameworkMapper Bundle
This assessment is part of the FrameworkMapper Bundle — one per-framework subscription that also includes Gap Optimization, the Threat-Gap Visualizer, the Incident Response Packet, and progress check-ins with phone photo evidence capture, across a 12-month term.
How Pricing WorksProgressive 10-Tier Structure
CIS Controls are organized into 10 progressive tiers based on security maturity, not cost or complexity. Each tier builds upon the previous, creating a natural implementation roadmap from foundational controls to elite security.
Start with Tier 1 to establish your security foundation, then progress through each tier as your program matures. Most organizations should aim to complete Tiers 1-3 before advancing to higher tiers.
Sources
- Center for Internet Security. CIS Community Defense Model v2.0. cisecurity.org
- Center for Internet Security. Texas Becomes Fifth Safe Harbor State, Cites CIS Controls in New Cybersecurity Law. cisecurity.org
- IBM Security. Cost of a Data Breach Report 2025. ibm.com/reports/data-breach
Ready to Assess Your Security Posture?
Try our CIS Controls assessment tool with a free trial. Create an account to save your progress and generate professional reports.
Contact sales at sales@frameworkmapper.com