CMMC Level 1 Assessment
Prepare for CMMC certification with our self-assessment tool covering the 15 foundational practices required to protect Federal Contract Information (FCI).
Why This Matters
The Contract You Can't Bid Without It
CMMC Level 1 isn't optional for DoD contractors handling FCI. The contracts — and the liability — are real.
CMMC Level 1 compliance is a prerequisite for all DoD contracts involving Federal Contract Information. Without it, you cannot bid — regardless of price or qualifications.
Source: DFARS 252.204-7012; DoD CMMC 2.0
of defense contractors are not yet CMMC-certified as the phased rollout accelerates. Early movers gain a direct competitive advantage in contract awards.
Source: OUSD(A&S) estimates1
Annual self-attestation in SPRS is required under FAR 52.204-21. A false attestation carries civil and criminal liability under the False Claims Act — the same statute used to prosecute federal fraud.
Source: DoD CMMC Program Rule; False Claims Act, 31 U.S.C. § 3729
A traditional CMMC L1 assessment is a significant investment, while the DoD contracts at risk are substantial. FrameworkMapper makes structured assessment accessible — a fraction of a single lost award.
Industry assessment market rates 2026
What is CMMC Level 1?
The Cybersecurity Maturity Model Certification (CMMC) Level 1 represents the foundational tier of cybersecurity practices required for organizations handling Federal Contract Information (FCI) in Department of Defense contracts.
15 Practices
A focused set of basic cyber hygiene practices that form the foundation of cybersecurity for DoD contractors.
Annual Self-Assessment
Level 1 requires annual self-assessment — no third-party certification needed. Results must be entered into SPRS.
FCI Protection
Designed to protect Federal Contract Information — information not intended for public release provided by or generated for the government.
6 Security Domains
CMMC Level 1 practices are organized into 6 security domains, each addressing a specific area of cybersecurity protection.
Access Control
Limit system access to authorized users, processes, and devices. Control what information users can access and what they can do with it.
Identification & Authentication
Verify the identity of users, processes, and devices before granting access to organizational systems.
Media Protection
Protect information system media containing FCI, both paper and digital, and limit access to authorized personnel.
Physical Protection
Limit physical access to systems, equipment, and operating environments to authorized individuals.
System & Communications Protection
Monitor, control, and protect communications at external and key internal boundaries of information systems.
System & Information Integrity
Identify, report, and correct system flaws in a timely manner. Provide protection from malicious code.
Who Needs CMMC Level 1?
DoD Contractors
Any organization that handles Federal Contract Information (FCI) as part of a DoD contract.
Subcontractors
Companies in the defense supply chain that receive FCI from prime contractors.
New DoD Bidders
Organizations preparing to bid on DoD contracts that will require CMMC certification.
Level 2 Preparation
Organizations using Level 1 as a stepping stone toward CMMC Level 2 certification.
How the Assessment Works
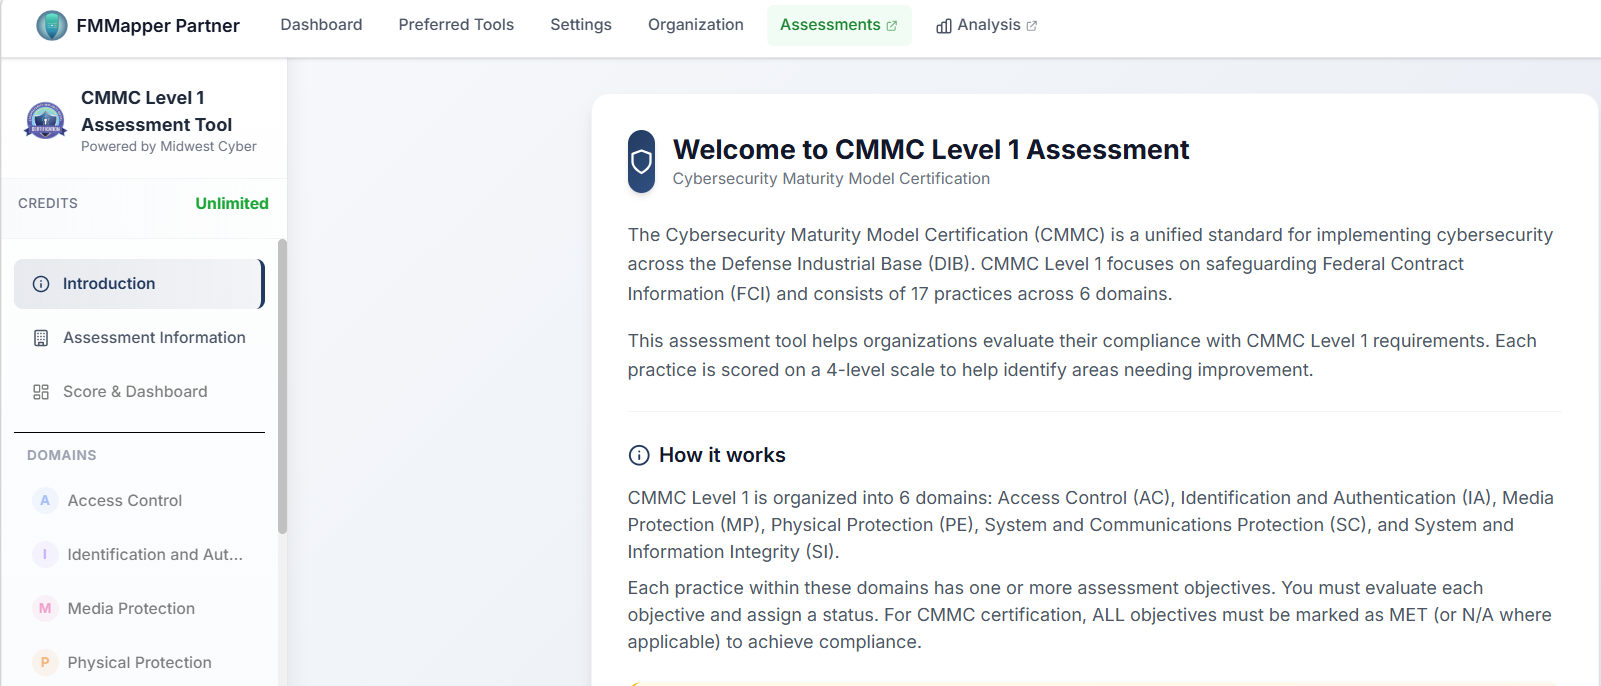
Our assessment tool guides you through all 15 practices with clear explanations and helps you document your compliance status for SPRS submission.
Select a Domain
Navigate through the 6 security domains, reviewing practices in each area.
Evaluate Each Practice
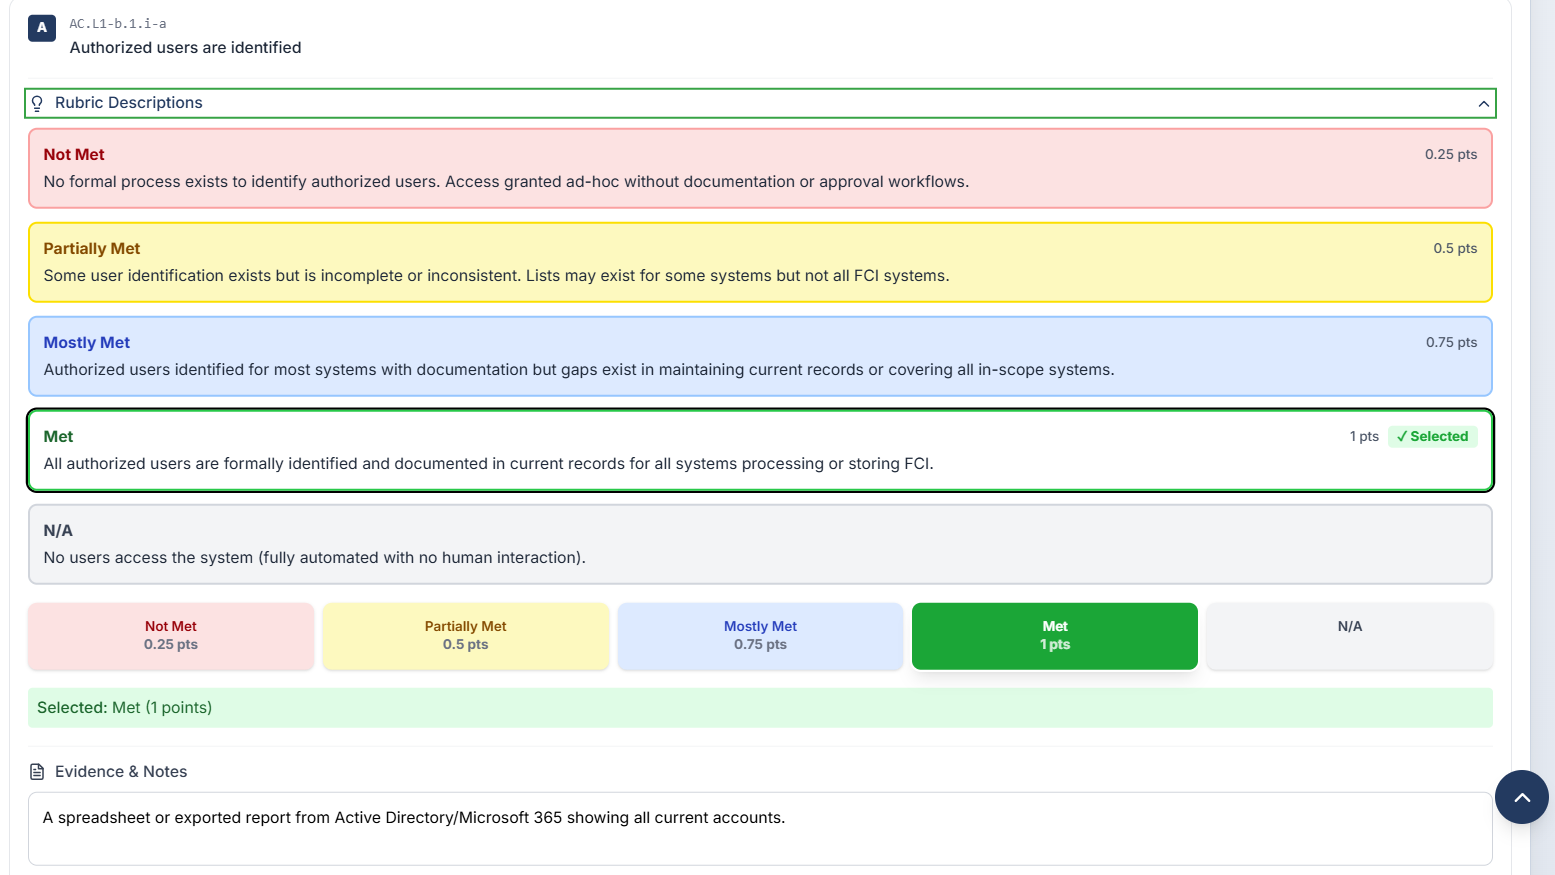
For each practice, assess your current implementation: Met, Partially Met, or Not Met.
Document Evidence
Add notes describing how you implement each practice and any supporting evidence.
Generate Reports
Download your assessment report for internal review and SPRS documentation.
Time Estimate
A complete Level 1 assessment typically takes 30-60 minutes for organizations with basic documentation already in place.
What to Have Ready
- Current access control policies
- Physical security procedures
- Antivirus/malware protection info
- User authentication methods
What You'll Receive
Generate comprehensive reports to document your CMMC Level 1 compliance status and support your SPRS submission requirements.
Assessment Report
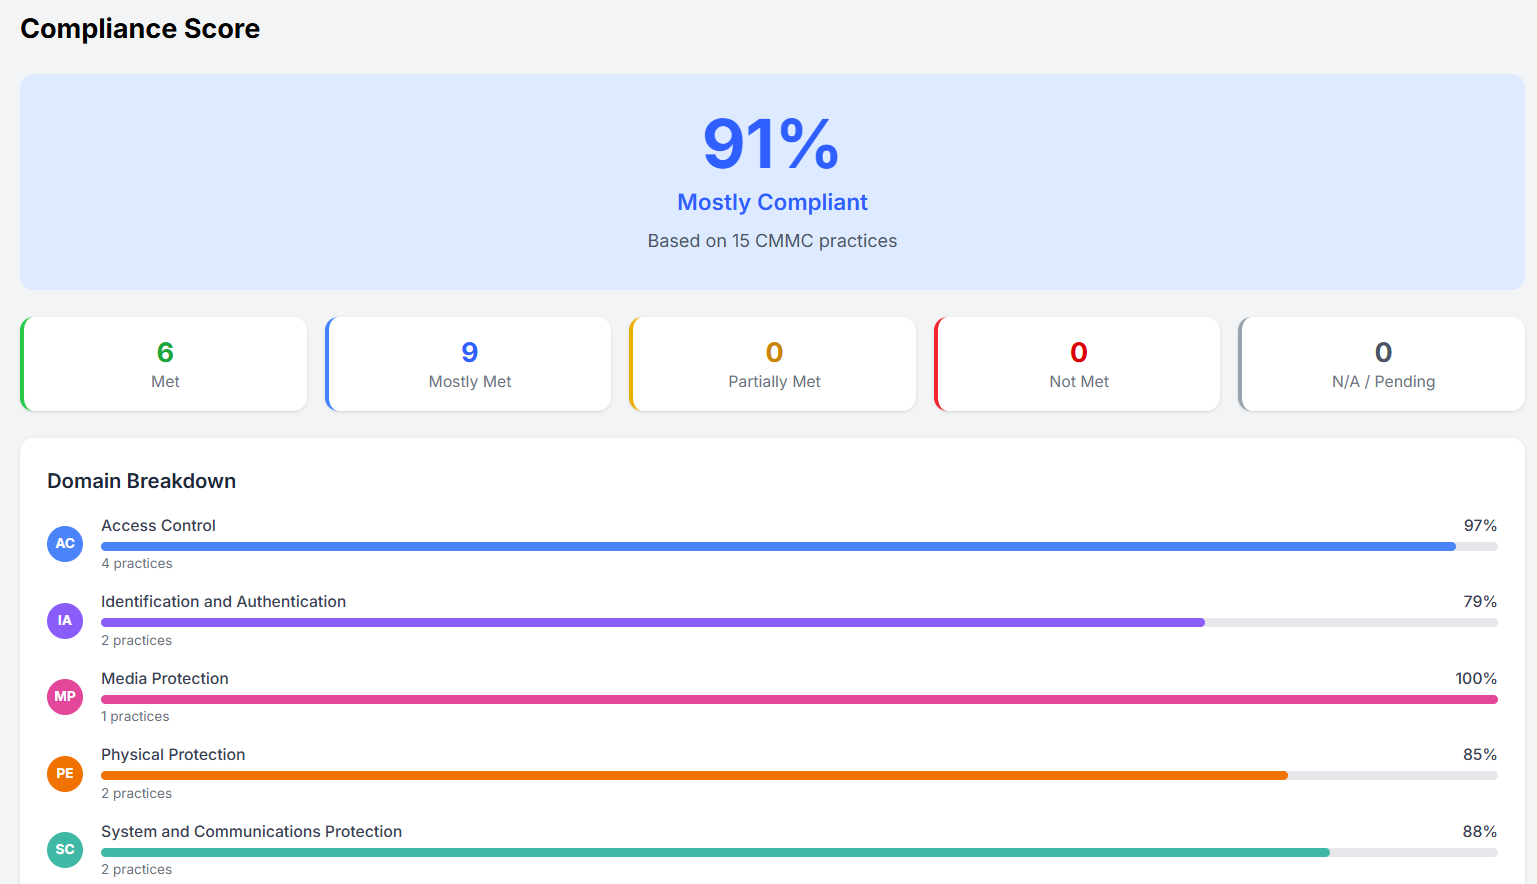
Complete assessment results showing compliance status for each practice, organized by domain with summary statistics.
- All 15 practices detailed
- Domain-by-domain breakdown
- Your implementation notes
SPRS Documentation
Supporting documentation formatted to help with your Supplier Performance Risk System (SPRS) score submission.
- Compliance status summary
- Assessment date tracking
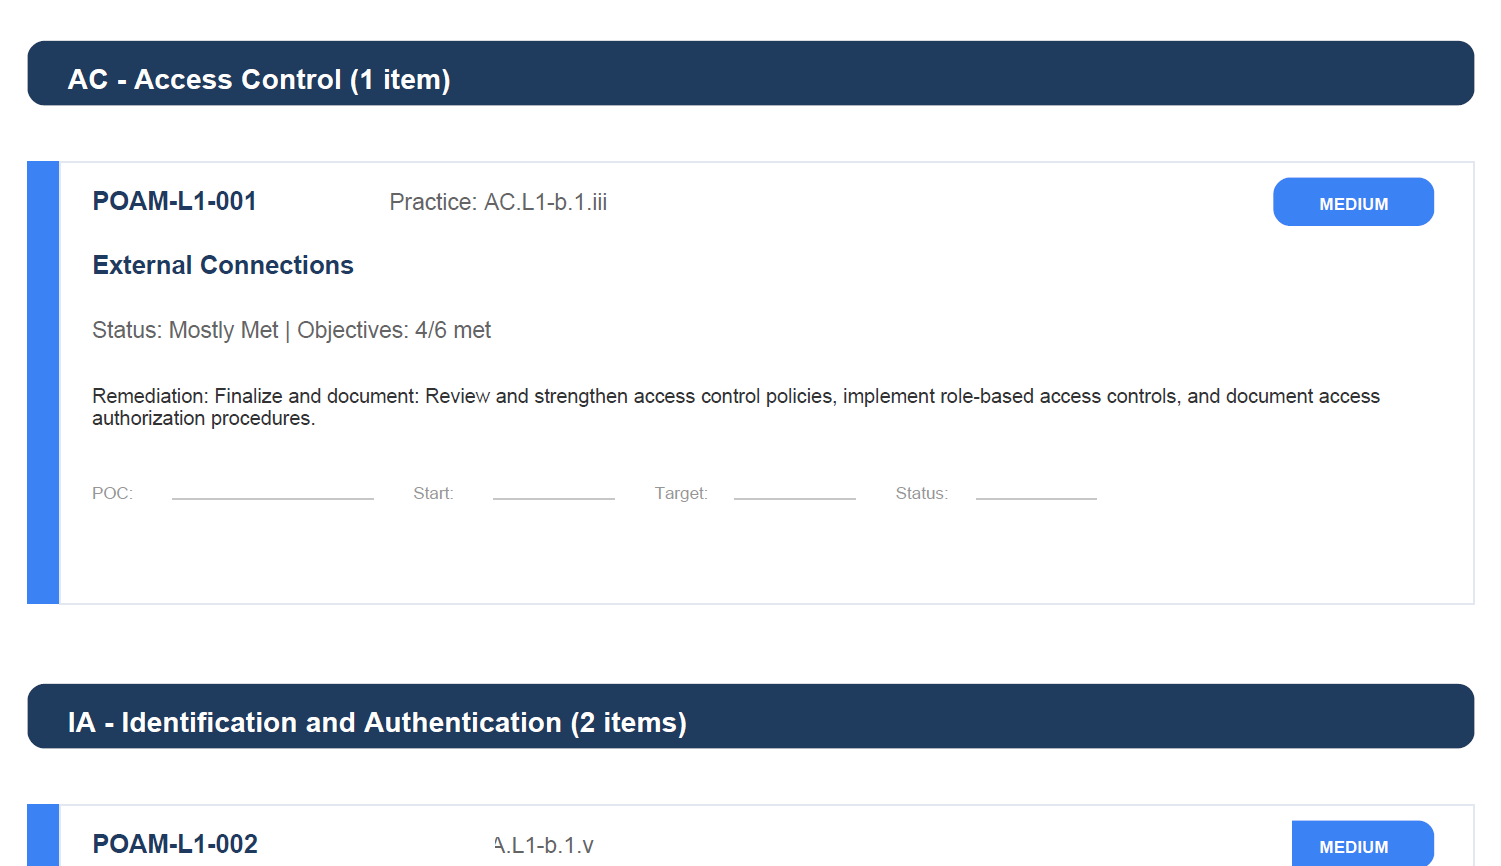
- Gap identification
Encrypted Backup
A password-protected JSON file containing all your assessment data. Use it to restore your assessment or transfer between devices.
- AES-256 encryption
- Complete data export
- Easy restore process
Beyond Compliance
See Your Results Through an Attacker's Eyes
Completing your assessment unlocks FrameworkMapper's threat-informed views — the same control scores, re-read against real adversary behavior from MITRE ATT&CK® and curated threat intelligence.
Threat Lens & Adversary Likelihood
Advanced reports that map your control scores to attacker techniques and rank which adversaries are most likely to succeed against you.
Threat-Informed Executive Report
A board-ready PDF with your Attack Surface Coverage Score (ASCS) and kill-chain exposure, computed from your actual answers.
Incident Response Packet
Your assessment answers and evidence pre-fill a Responder Brief and evidence bundle, so responders can act on day one. Learn more
Included With Your Subscription
Runs on the FrameworkMapper Bundle
This assessment is part of the FrameworkMapper Bundle — one per-framework subscription that also includes Gap Optimization, the Threat-Gap Visualizer, the Incident Response Packet, and progress check-ins with phone photo evidence capture, across a 12-month term.
How Pricing WorksLevel 1 vs Level 2: Which Do You Need?
The right CMMC level depends on the type of information you handle in your DoD contracts.
Federal Contract Information (FCI)
- 15 practices across 6 domains
- Annual self-assessment
- No third-party certification required
- Basic cyber hygiene
Controlled Unclassified Information (CUI)
- 110 practices across 14 domains
- Triennial third-party assessment (C3PAO)
- Aligned with NIST SP 800-171
- Advanced cyber hygiene
Sources
- Office of the Under Secretary of Defense for Acquisition & Sustainment. CMMC Program estimates. acq.osd.mil/cmmc
Ready to Assess Your CMMC Level 1 Readiness?
Try our CMMC Level 1 assessment tool with a free trial. Document your compliance status and prepare for your SPRS submission.
Contact sales at sales@frameworkmapper.com